Holy shit.
From a brief scan it looks like the paper concentrates on recovering a numeric pin, but these attacks never get worse, only better, so I assume full keyboard access is not too far off.
What's the defense? Have your phone manage the passwords and unlock via fingerprint?
Well if one modifies the channel state information in an unpredictable manner while performing sensitive operations, it becomes very difficult to extract any information. The simplest way to do this might be to fidget. Use one hand to type and another hand to fidget with something.
A more high tech method would be to use a modulated wifi reflector that is randomly modulated.
One should also watch out for wifi hotspots with ominously pointed directional antenna
The defence is definitely to not use public wifi. This technology works because they can identify small target windows (e.g. you just accessed a URL to login to your bank account) in which to make and process these measurements. Any kind of abnormal obfuscation of your device should introduce enough noise to prevent this attack from generating any meaningful data from the victim, but I'm running on assumption.
Couldn't this work against any wifi? Impersonating a public access point gives you some extra unencrypted information so you know the server IP and can more easily infer when a password is being entered, the same things you conceal by using a VPN over public wifi.
But what stops a passive wifi observer who can guess those things or already knows them?
I think this is pretty hand-wavey and requires a lot assumptions to be true.
Also: "We collected training and testing data from 10 volunteers." Not a statistically useful sample set.
Under very controlled environments, measuring signal deltas may be possible- but I would like to see sample data that suggests high success rates before I think this is worthy of concern.
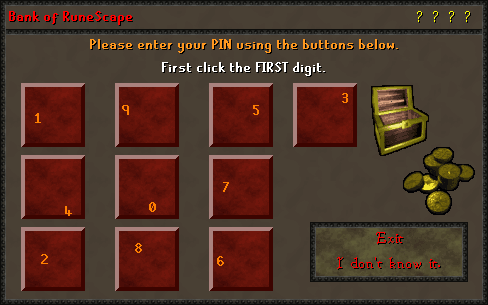
Anybody who plays Runescape will recognize this. They have a pin you can set to gain access to your in game bank. It has a fair few security features to combat keyloggers which were (and still can be) a major issue.
Some security features I can recall.
Random layout of the numbers on both the button itself and which button has which number. This is shuffled on every click.
Upon clicking all numbers and the mouse pointer vanish. This prevents screenshots taken on clicks by some keyloggers from working.
No keyboard input. Annoying but needed to combat keyloggers.
My bank did that with a JavaScript number pad. They went back to a standard password field with the new design of the site a couple of years ago. That made me feel less safe because I understood why the were complicating the input.
Another strategy I've seen is to ask some random digits of a longer PIN, with a mask to fill out.
Some banks (e.g. Barclays) use a card reader that generates a unique key each time. Since this also requires that you have your card to log in, it's my understanding that this offers massively improved security.
Touch typing on a flat, featureless surface? Best of luck with that. I tried, and tended to drift off-center within a few tens of keystrokes. The F and J nubs on physical keyboard are there for Good Reasons - but even without, feeling where exactly you are striking the key (center or corner) gives you feedback to reposition. Touchscreen gives you nothing.
The process of connecting to public wifi is risk. Most public wifi networks have a landing page that you have to click through before proceeding/granting you access. That page could have a malicious script.
Last year after a trip in Germany, my older iPhone had a random password saved in Safari settings. On top of that, every time I tried to delete the password, it would reappear when I went back (iCloud sync was off, etc.). I don't remember browsing anything out of the ordinary, but did connect to a bunch of public wifi spots. Here's to hoping it was just a really persistent ad-tracking method.
I generally don't browse on my phone, so if I'm opening up Safari on a public network, it's to a known site or bookmark to quickly reference something (e.g. transit map, exchange rate). It's totally possible an ad on the NYT or Bloomberg has some malicious Javascript, but currently I'm naively assuming otherwise.
Also, I think many people on their phones will connect to a public hotspot just to check Facebook / Instagram / Snapchat these days and not much else.
For the second one, I believe you can still ID what sites a user is likely using if you're in the middle, regardless of https, via eg reverse IP lookups- just not what they're sending to that site. A VPN covers that.
In many (most?) countries mobile data is cheaper than wired connections, but obviously with worse latency.
Slower too maybe, but we're long past the point it really matters, except for latency sensitive applications. 50+ Mbps is just plenty for most applications.
Only real need of wifi to save some battery power and maybe to get better latency and jitter for VoIP and interactive applications.
AFAIK, US and UK are still pretty bad. I guess they have to limit bandwidth and data volume to be able to, ahem, listen to their customer.
The attack presented in this paper relies on the user connecting to the wifi hotspot. This is necessary so that they can figure when a sensitive operation is happening.
Without this information, it is difficult to determine if the user is inputting a password. In addition, if we know the user is using the bank of america app, and we know that the app uses a specific key lay out, it becomes a lot easier to figure out what keys they are pressing.
There is no reason that the other technique they discussed, which does not require the target to connect to a specific wifi hotspot, could not be improved though.